In brief
On 5 November 2026, EU cyber authorities, including ENISA and Europol's EC3, issued a joint alert over a new wave of attacks that struck refrigeration systems on 1 and 2 November. Organisations are urged to consult national advisories and comply with the EU Cyber Resilience Act’s reporting rules and forthcoming security requirements set to take effect on 11 December 2027.
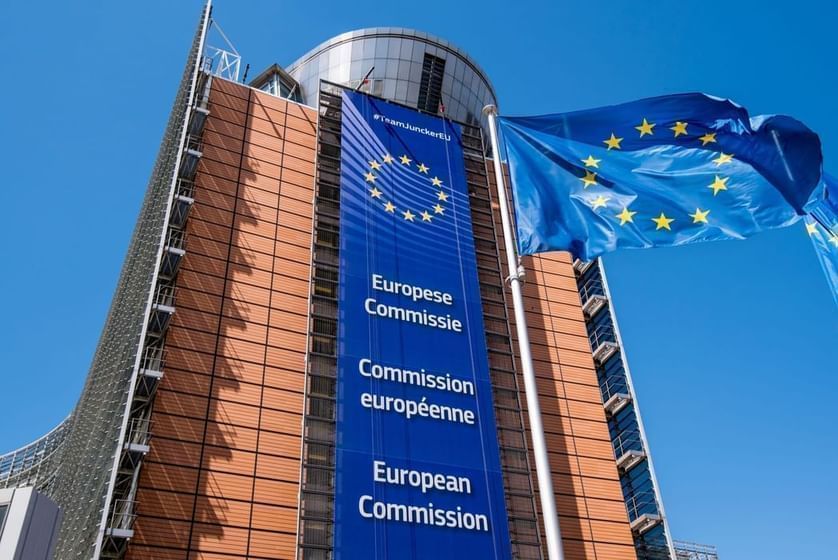
In Brussels on 5 November 2026, European Union cyber agencies issued a joint alert warning that a new wave of cyberattacks had struck refrigeration systems on 1 and 2 November, urging organisations across the bloc to take immediate action to reduce exposure.
The warning, released by the European Union Agency for Cybersecurity (ENISA), the European Commission, Europol’s European Cybercrime Centre (EC3), the EU CSIRTs Network and the EU‑Cyber Crisis Liaison Organisation Network (EU‑CyCLONe), highlighted that the incidents were being investigated by affected member states, which were also offering guidance and monitoring developments.
Member‑state national cybersecurity response teams and crisis management authorities are coordinating closely, exchanging information to track the attacks and support a unified response across the European Union.
ENISA and its partners have urged organisations to consult the latest security advisories issued by national cybersecurity response teams and made available through ENISA’s advisory collection.
Hardware and software manufacturers were reminded that, under the EU Cyber Resilience Act, they must report severe incidents and actively exploited vulnerabilities through the Act’s Single Reporting Platform, a requirement that has been in force since 11 September 2026.
The Act’s main cybersecurity provisions will come into effect on 11 December 2027, mandating manufacturers to embed security into product design, provide ongoing support throughout product lifecycles and address vulnerabilities without delay.
Organisations that fall under the EU’s Network and Information Security Directive (NIS2) are also required to implement robust cybersecurity risk‑management measures and to report significant incidents to the relevant national authorities or computer security incident response teams.
ENISA emphasises that it continues to promote secure‑by‑design and secure‑by‑default principles through technical advisories, guidance and information‑sharing initiatives aimed at strengthening cybersecurity across the Union.
As the new wave of attacks demonstrates, refrigeration systems—integral to cold‑chain logistics and food safety—have become a new target for cybercriminals, underscoring the urgent need for compliance with EU cyber‑resilience frameworks and the importance of cross‑border collaboration.